Cloud & DevOps Engineer who designs, automates and secures production-grade cloud infrastructure on AWS and Azure. Hands-on building containerised microservices on Kubernetes (EKS), provisioning infrastructure as code with Terraform, and delivering CI/CD pipelines with GitHub Actions and Jenkins. Practises DevSecOps end-to-end — shift-left security scanning, least-privilege IAM, and full observability with Prometheus and Grafana. Backed by 9+ years of engineering in high-reliability offshore environments, bringing an automation mindset, operational rigour and strong problem-solving to every deployment.
Four end-to-end builds, ordered from focused infrastructure automation through to a full production-grade Kubernetes platform. Each links to its source repository and a complete engineering report.
01 Project 01
Terraform S3 Automation with GitHub Actions
Infrastructure as Code · CI/CD · AWS
A production-grade Infrastructure-as-Code workflow that provisions a hardened Amazon S3 bucket entirely through CI/CD. Every change is reviewed as a pull request, planned automatically, and applied only on merge to main — no console clicking, no drift.
Terraform module provisioning S3 with versioning, server-side encryption, full public-access block, lifecycle rules, access logging and a production tagging standard.
Remote state on S3 with DynamoDB state locking — safe concurrent runs across a team.
GitHub Actions pipeline running fmt → validate → plan on every pull request and apply only on merge to main.
AWS credentials injected through GitHub Actions Secrets — zero credentials in source control.
Jenkinsfile included so the same IaC ships through either orchestrator.
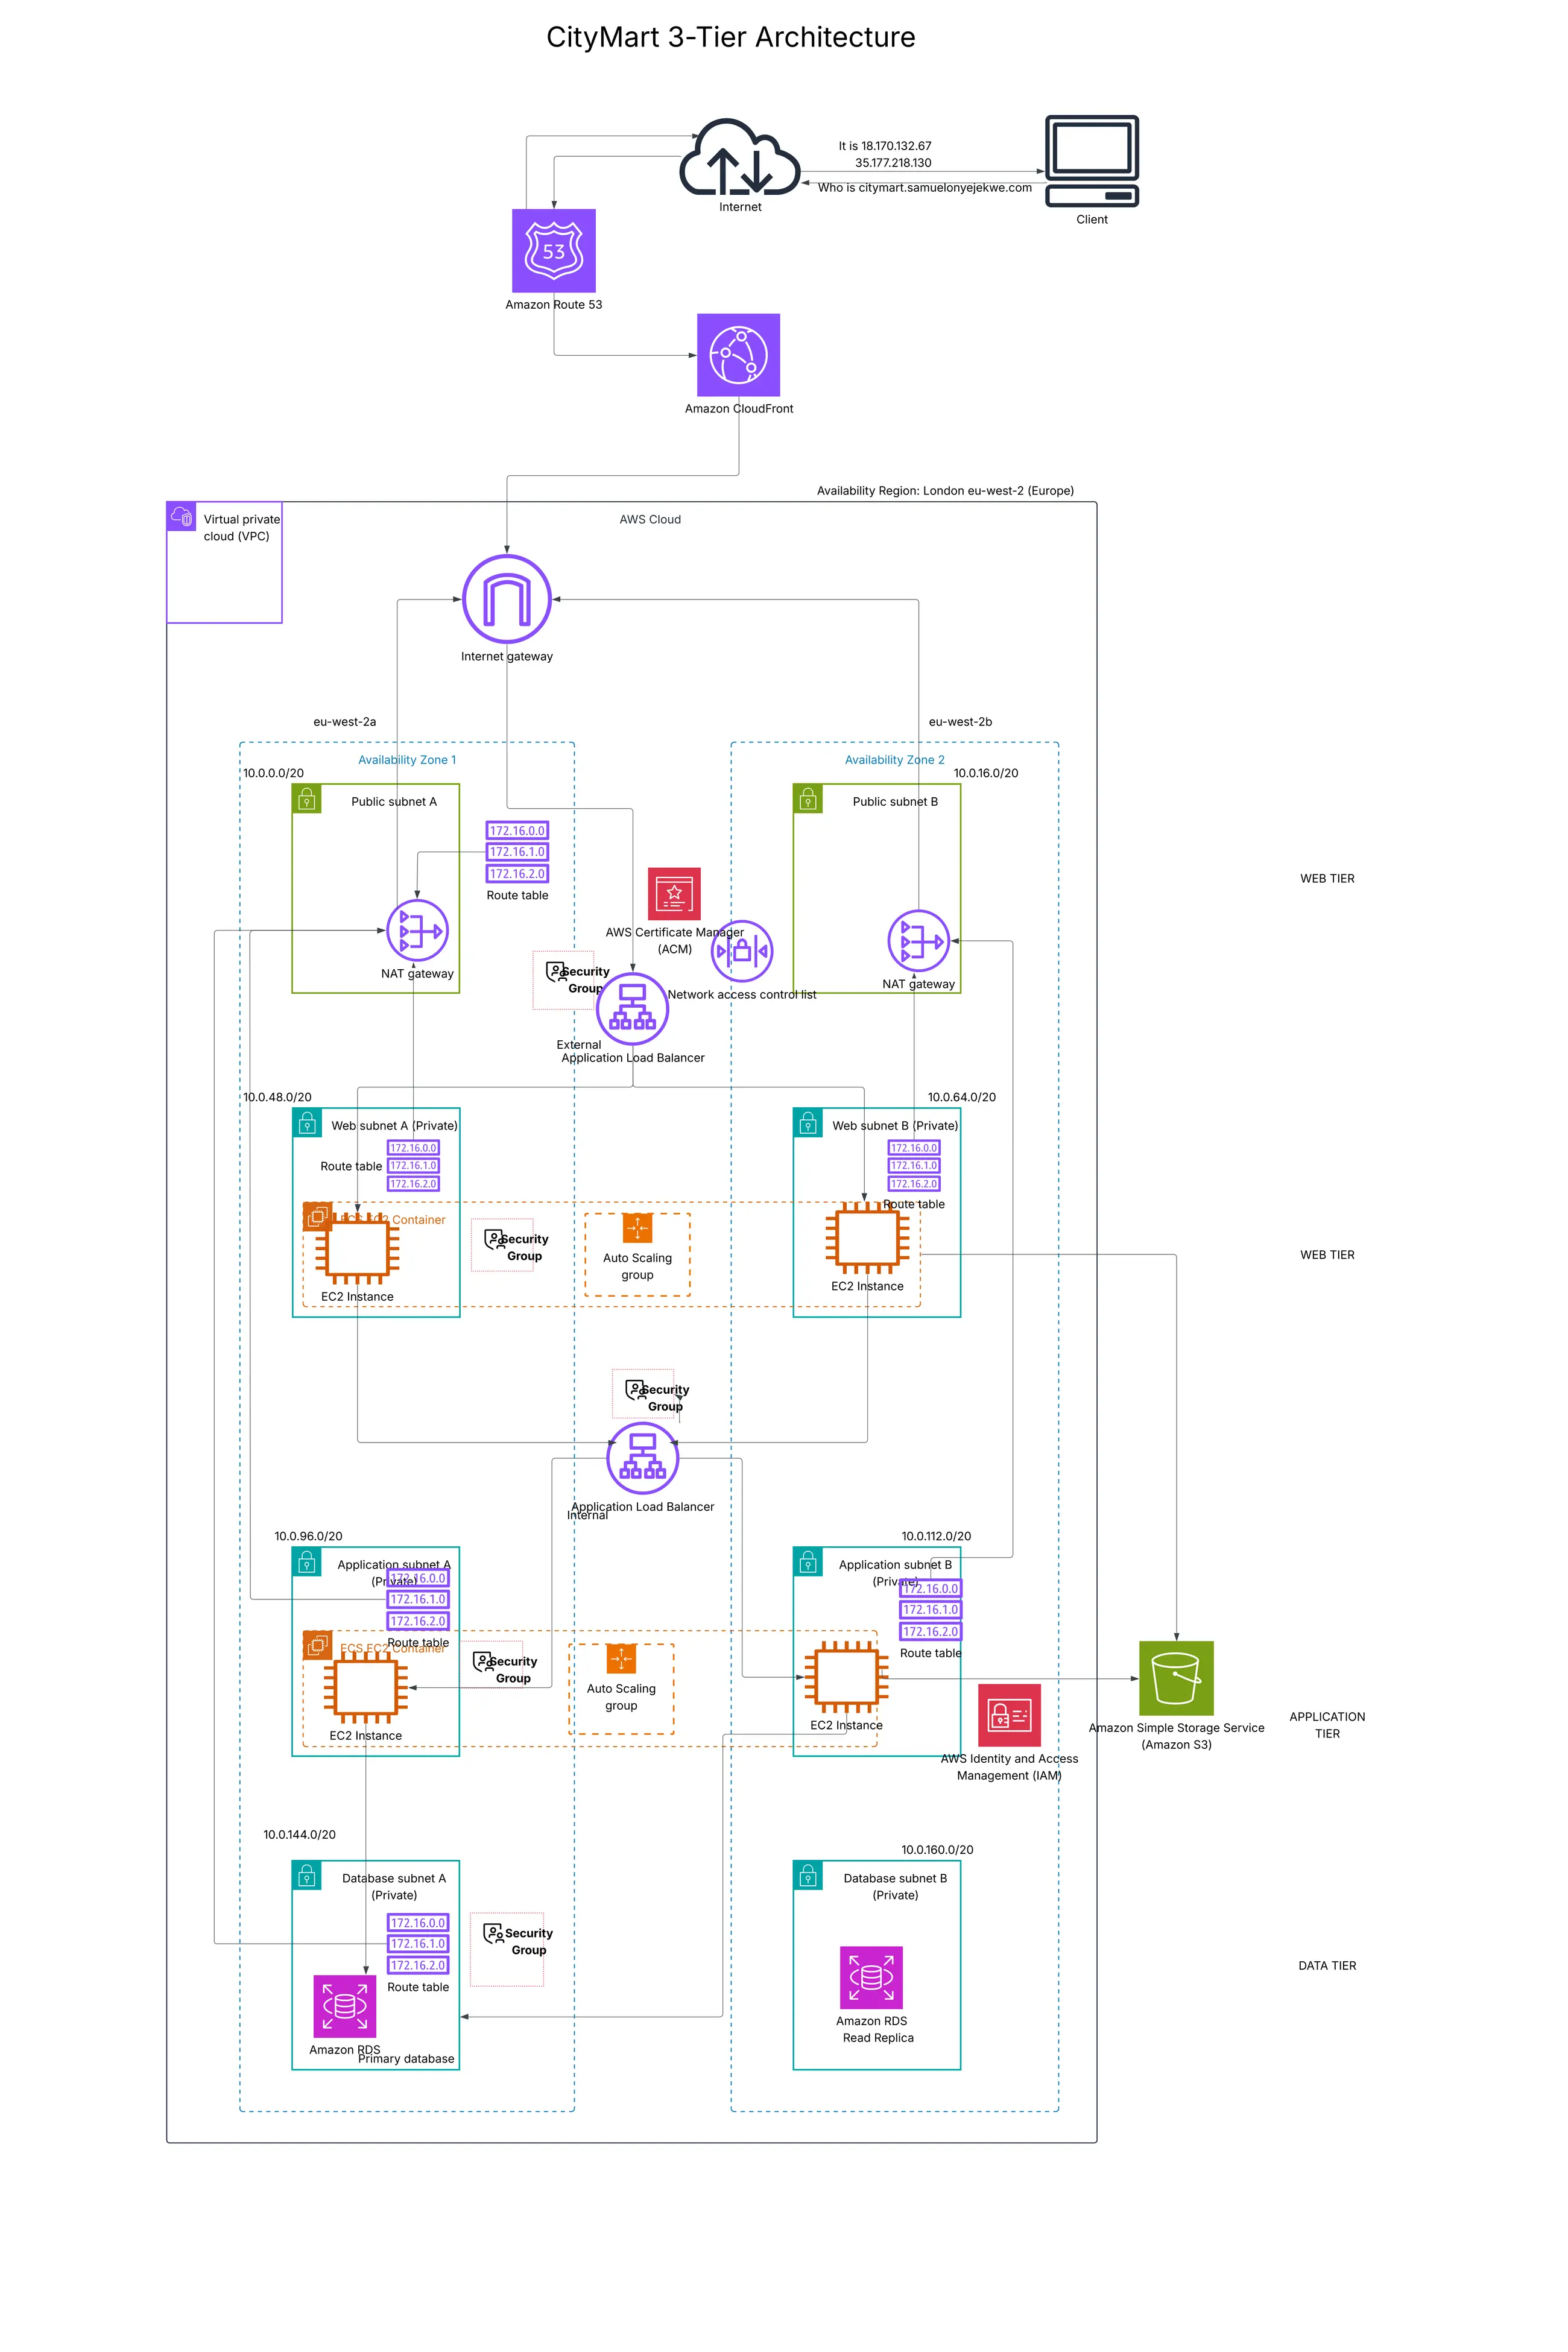
CityMart Online — Highly Available 3-Tier AWS Architecture
High availability · Network segmentation · AWS
A fault-tolerant three-tier e-commerce platform spanning two Availability Zones in eu-west-2, with every tier isolated in its own subnet and no single point of failure. Built once by hand to prove the architecture, then re-provisioned as Terraform IaC.
Custom VPC (10.0.0.0/16) with public, private-web, private-app and private-database subnets across two AZs; one NAT gateway per AZ to remove cross-AZ dependencies.
Web tier (Nginx) behind a public ALB, application tier (Apache/PHP) behind an internal ALB, data tier on Amazon RDS/Aurora MySQL Multi-AZ — strict security-group chaining between every hop.
Auto Scaling Groups keep both compute tiers self-healing; application code distributed from S3 so instances are fully ephemeral and replaceable.
Route 53 DNS with ACM TLS termination and an HTTP→HTTPS redirect; CloudFront in front for global cache and latency reduction.
Administrative access through SSM Session Manager — no bastion host and no open SSH port.
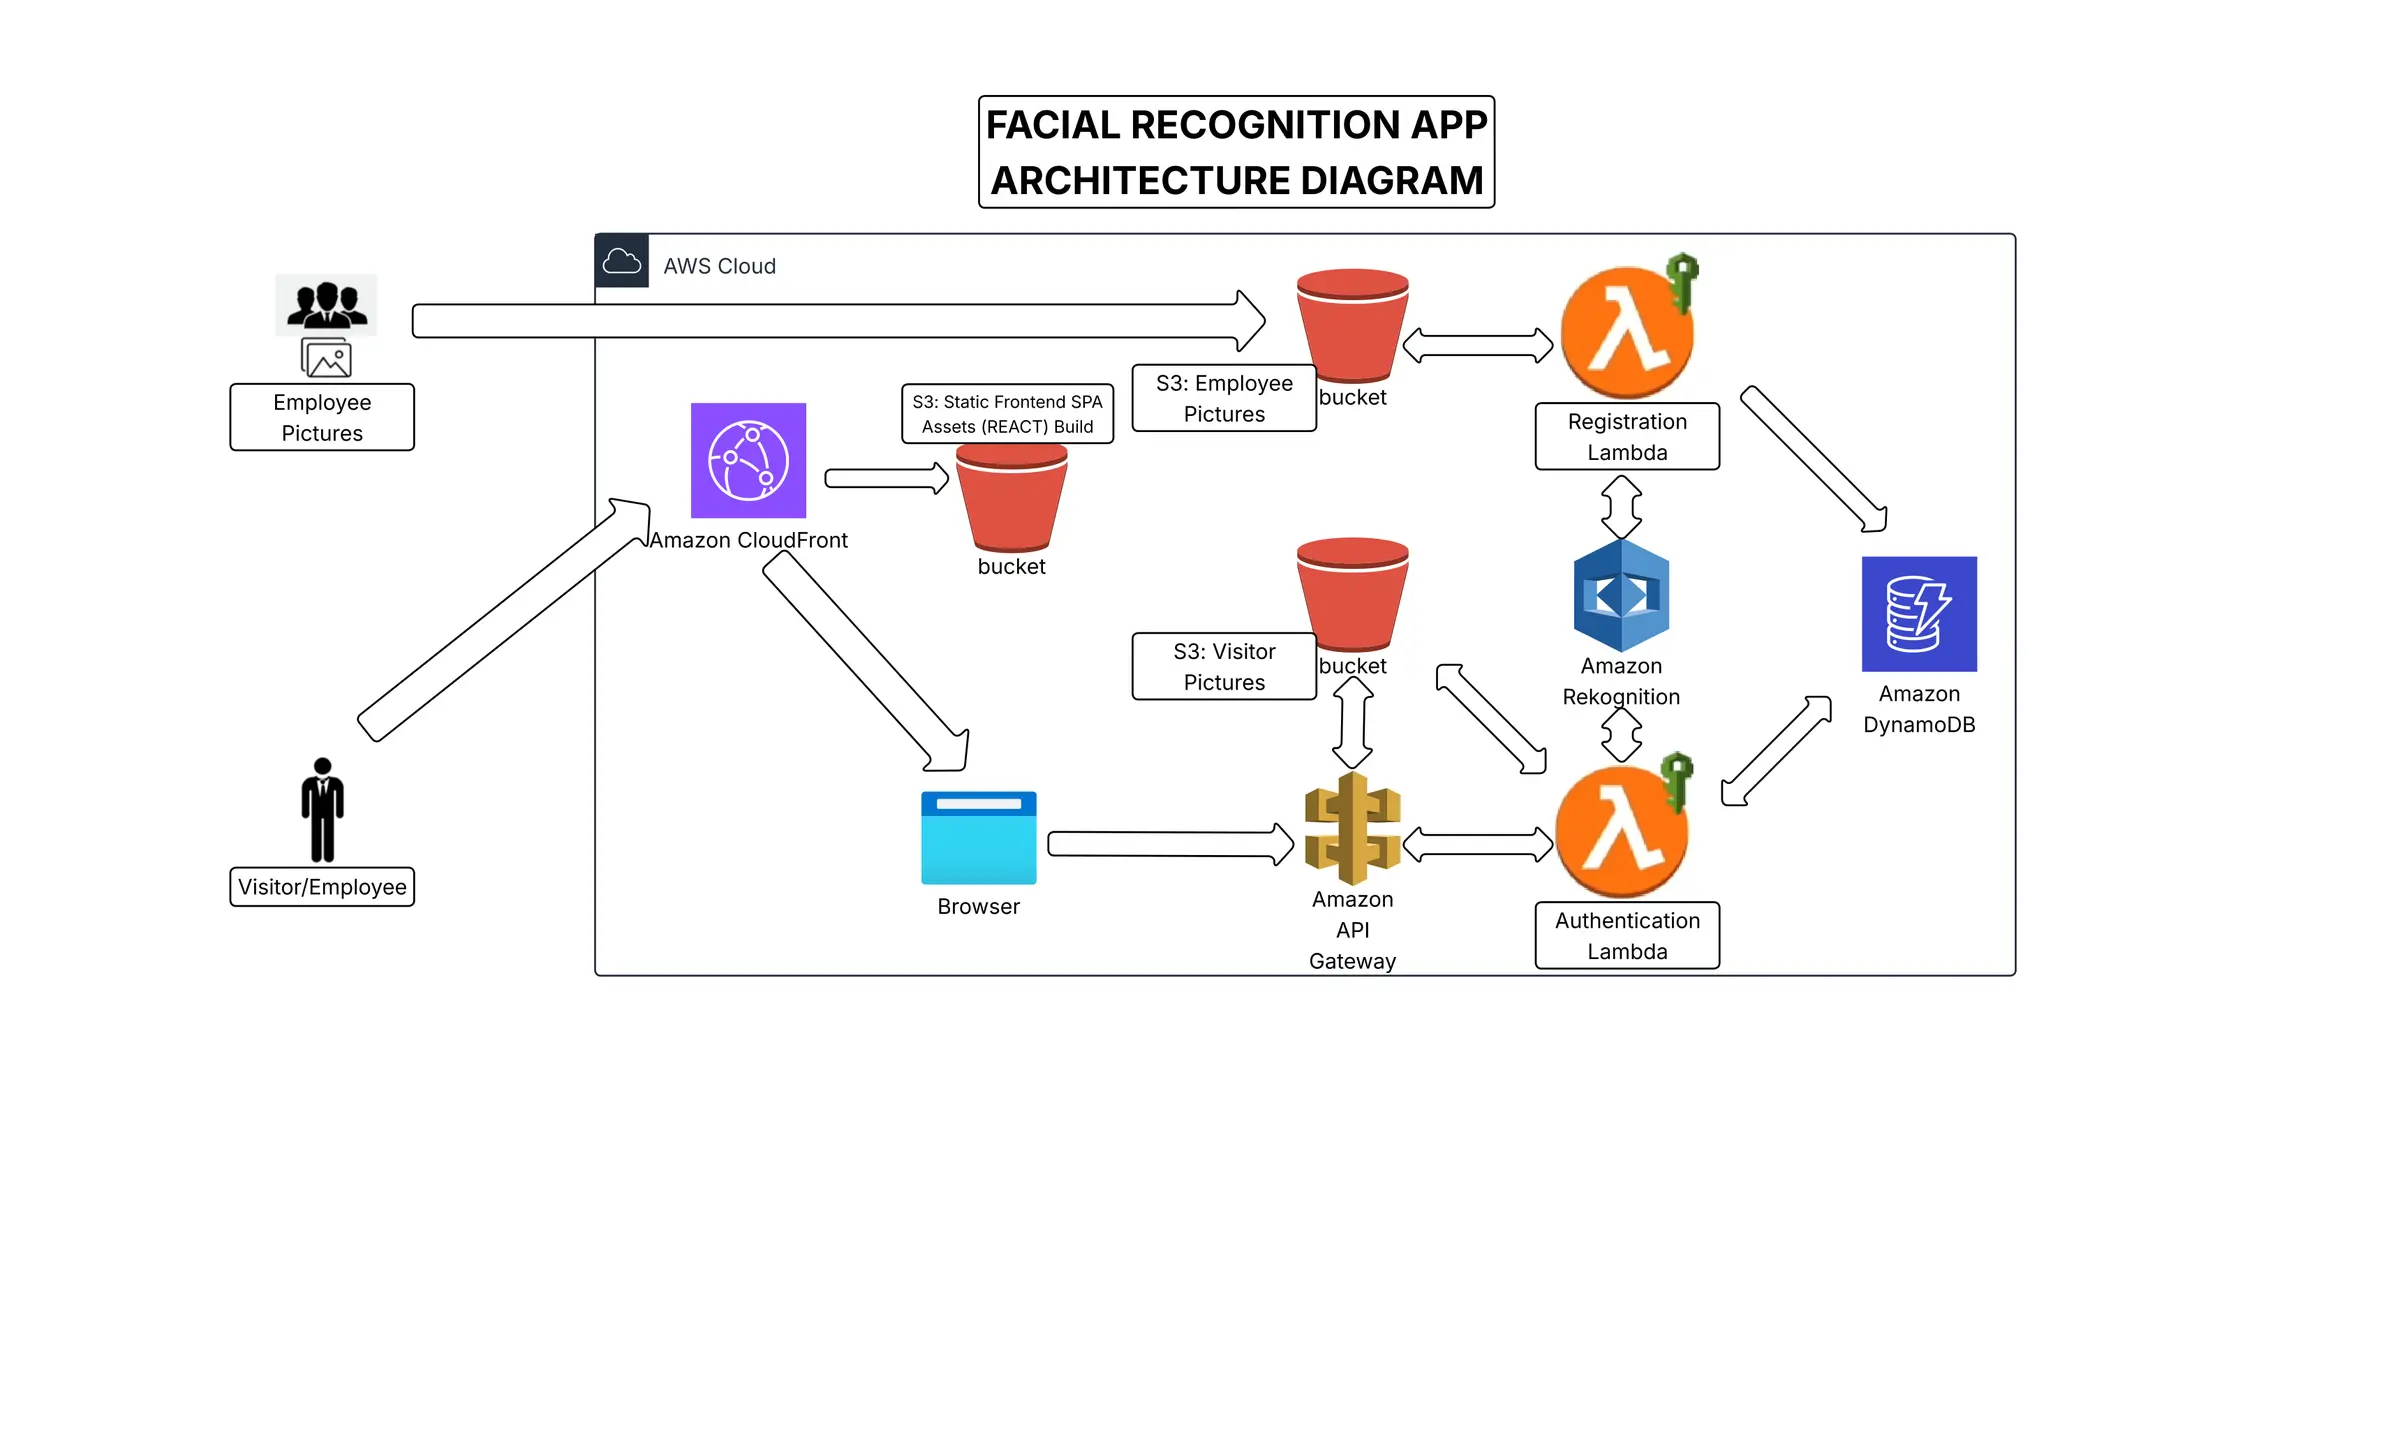
A fully serverless identity-verification system that replaces access cards and PINs with face-based authentication. Two independent workflows — event-driven registration and API-driven authentication — with zero servers to patch or scale.
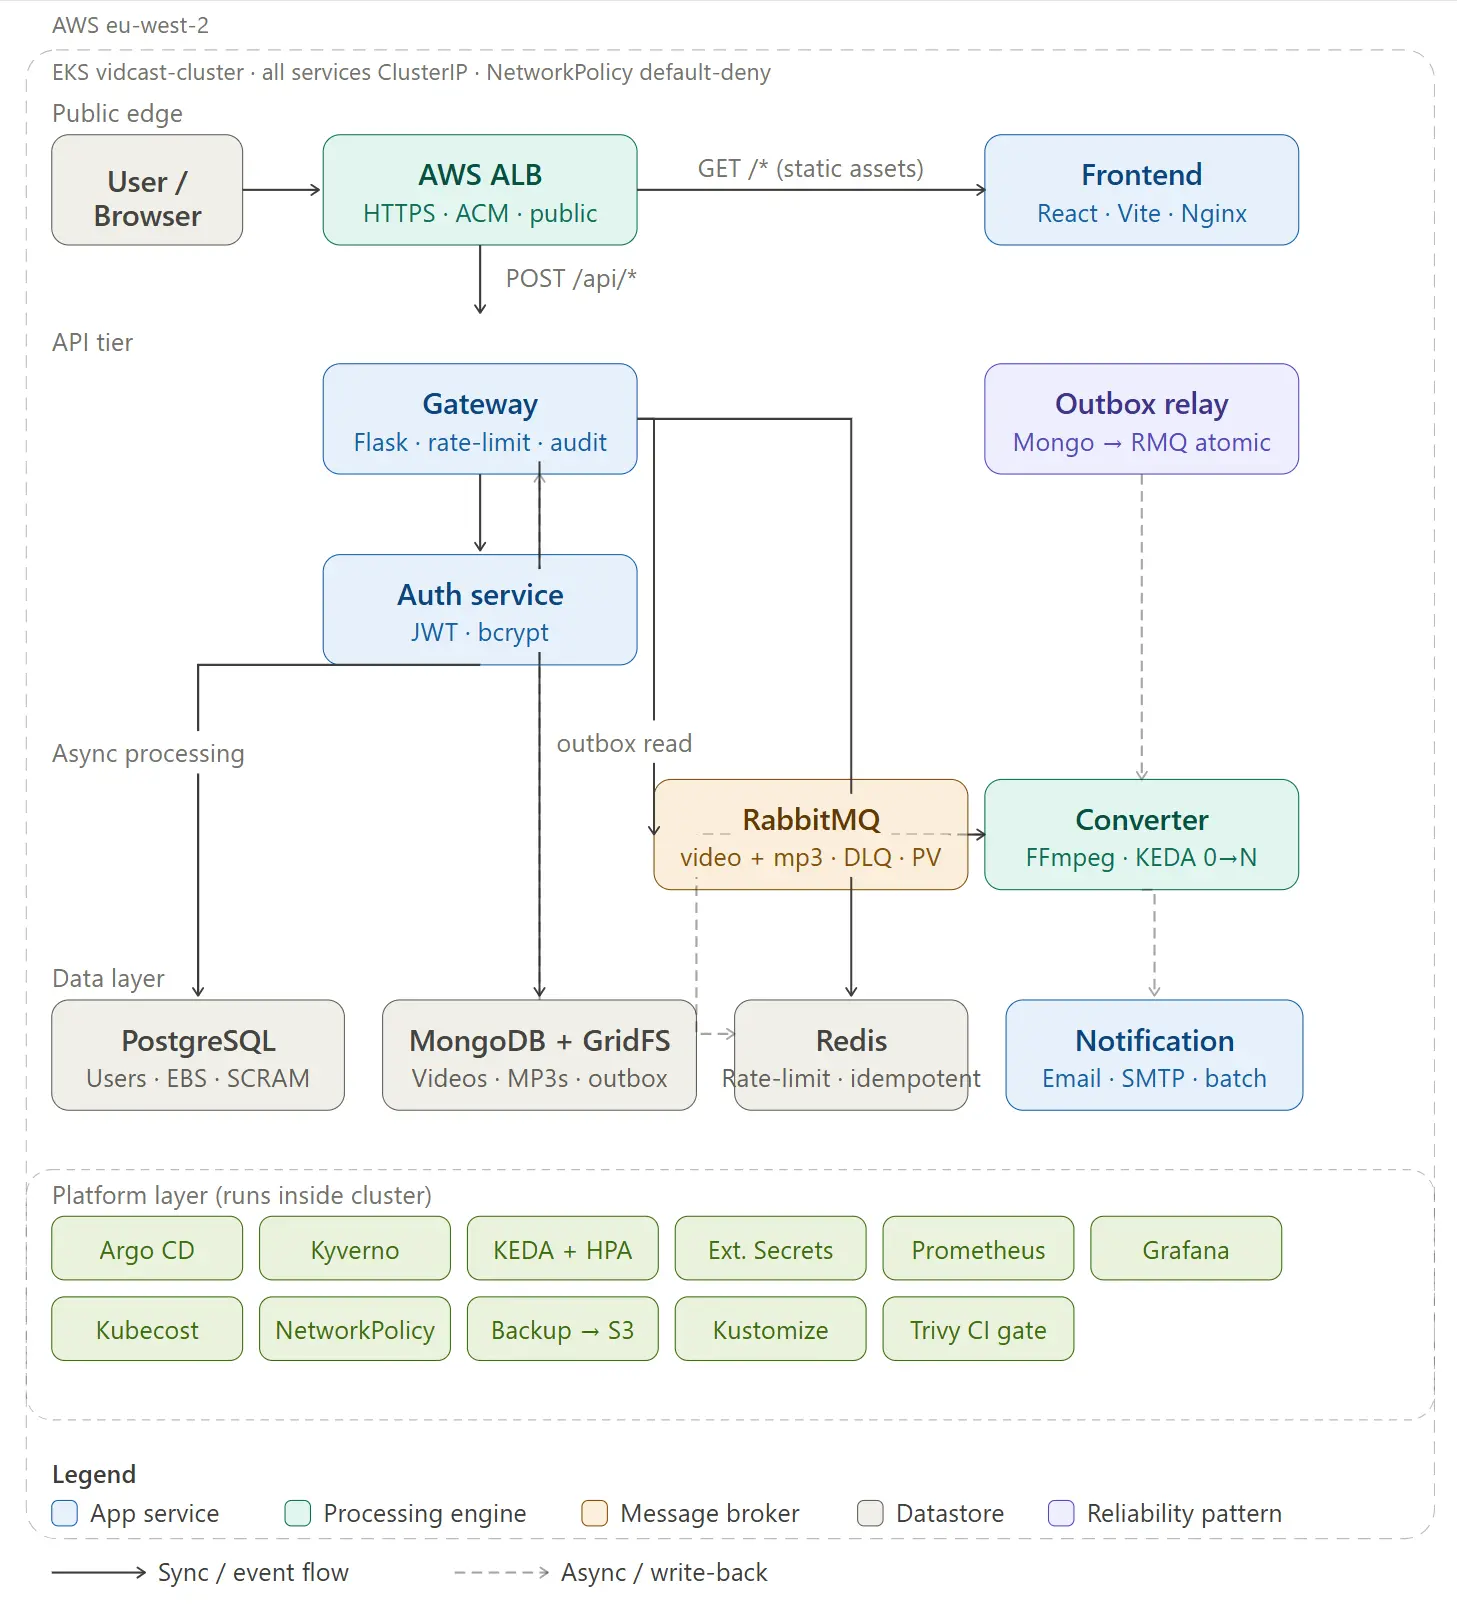
VidCast — Video Processing Microservices on AWS EKS
Kubernetes · DevSecOps · GitOps · Flagship
A production-grade, event-driven platform converting video to podcast-ready MP3 on Amazon EKS. Built for a realistic client — a London podcast company whose manual FFmpeg workflow was consuming roughly £100,000 a year of producer time and scattering client content across personal drives and third-party sites.
Five Python microservices (Gateway, Auth, Converter, Notification) plus a single-replica outbox relay on Kubernetes 1.29 (AWS EKS), fully provisioned with Terraform.
Store-and-queue pipeline: upload returns 202 in milliseconds and conversion happens asynchronously through RabbitMQ, with dead-letter and retry queues plus Redis deduplication for idempotency.
Event-driven autoscaling with KEDA on RabbitMQ queue depth (scale 0→N, then back to zero when idle) alongside HPA on the API tier.
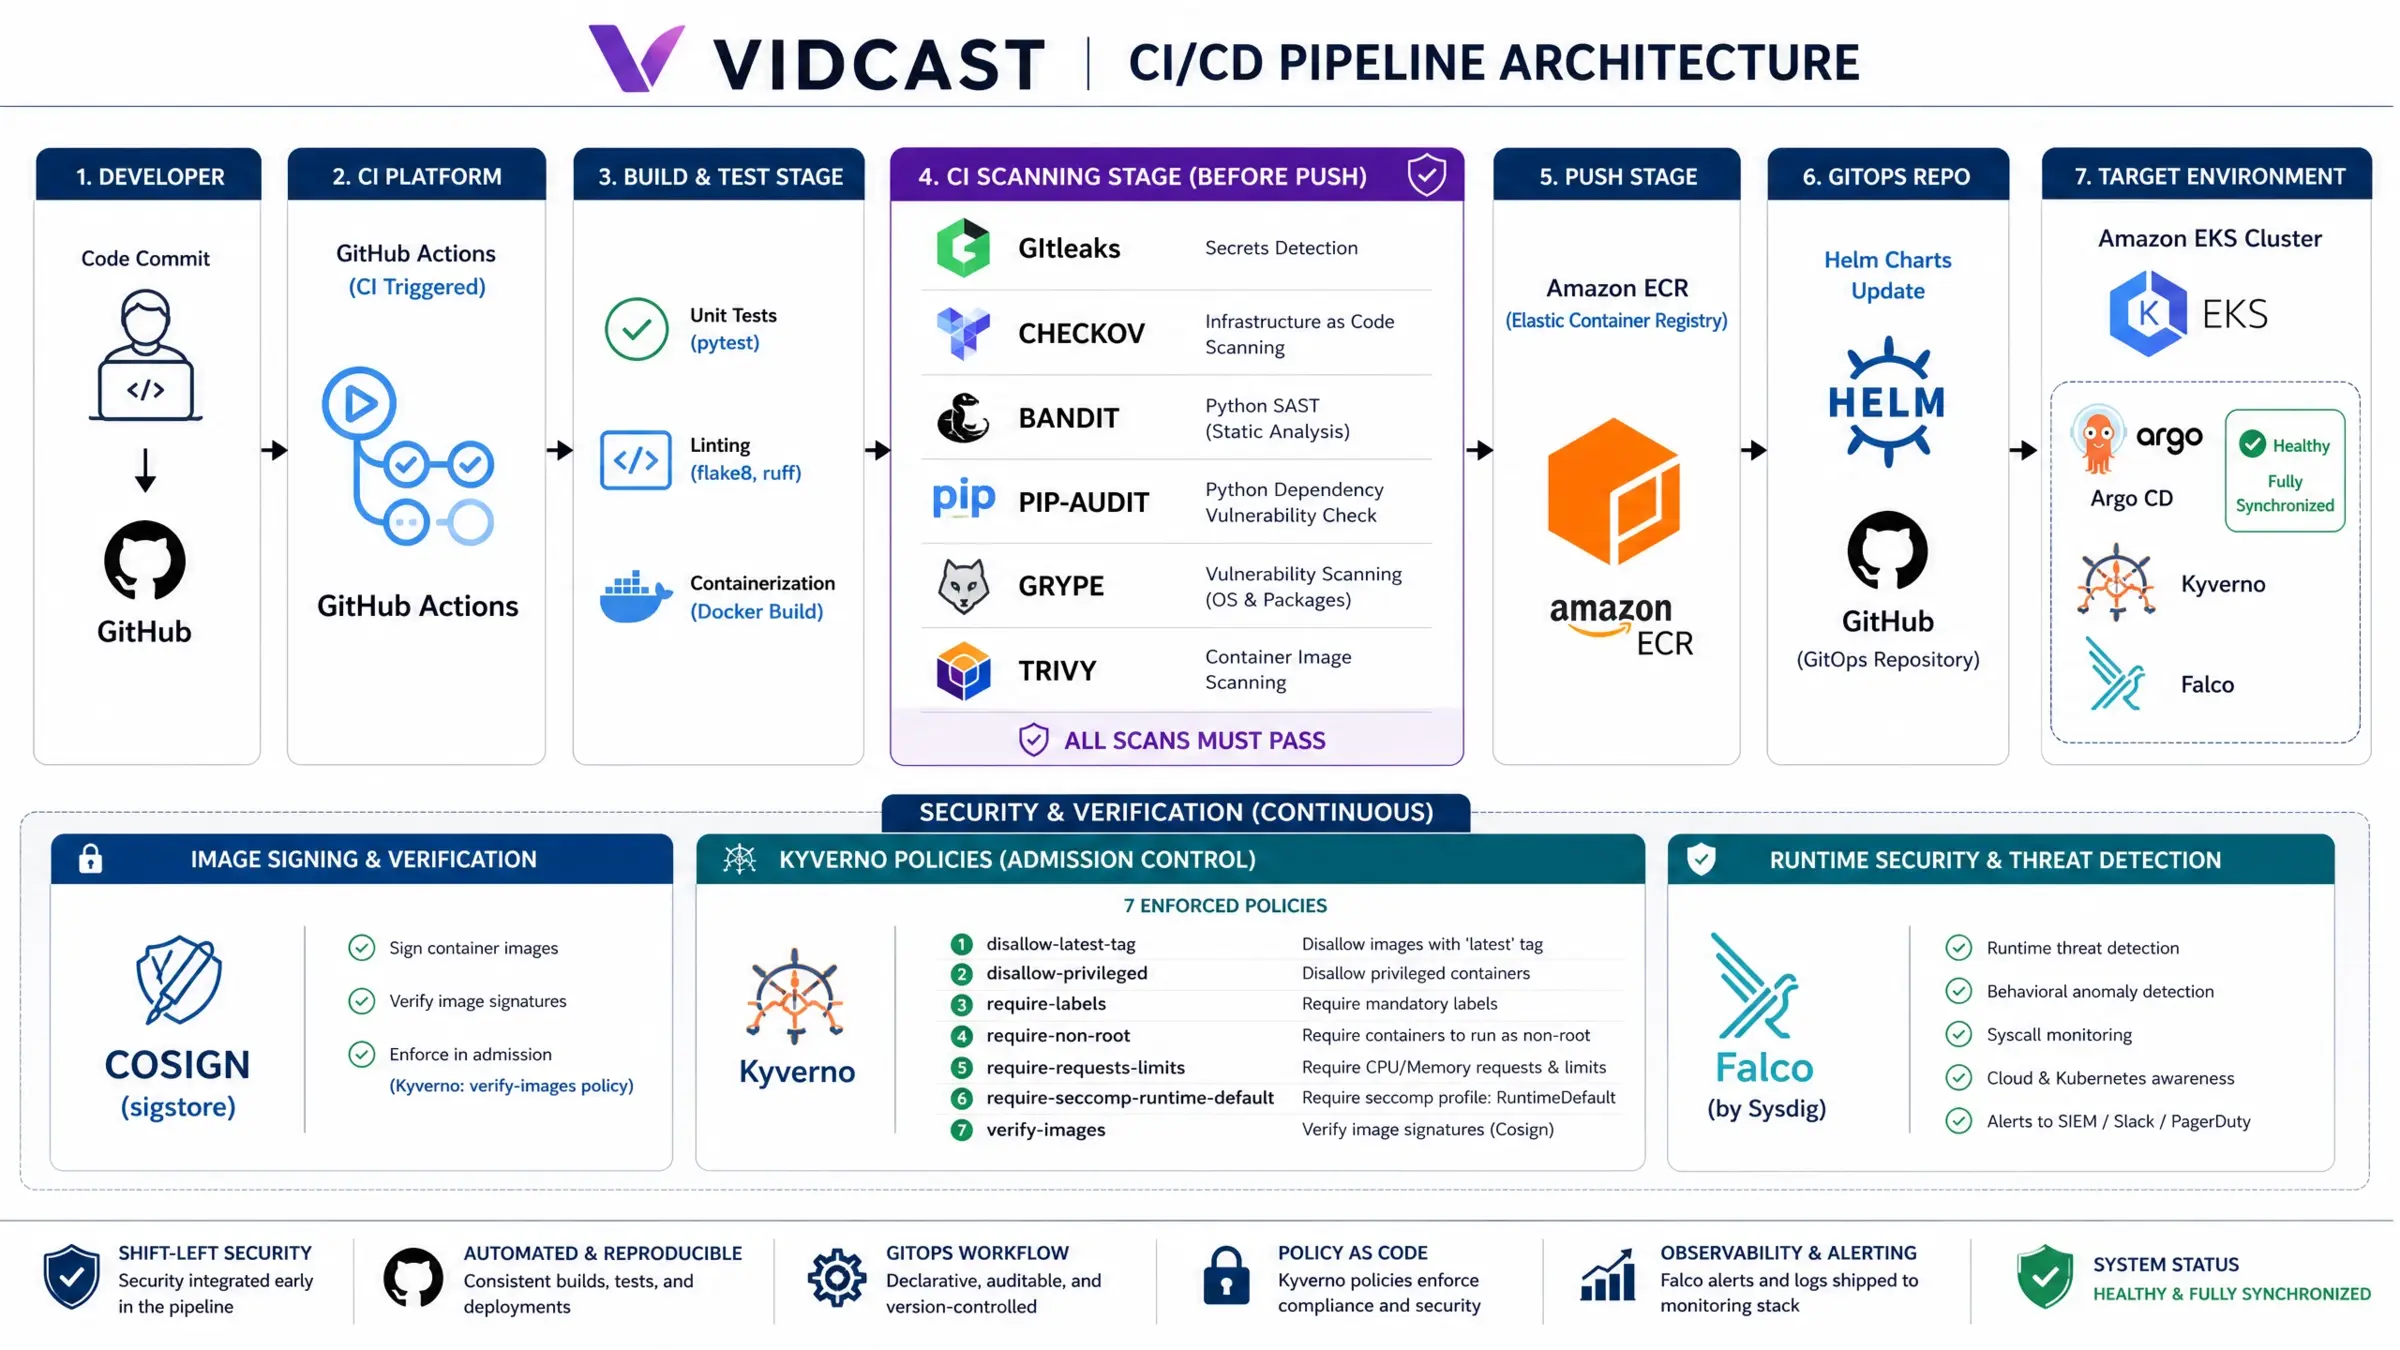
20+ GitHub Actions workflows and a Jenkins pipeline with a shift-left Trivy gate and Gitleaks secret scanning; Argo CD GitOps delivery behind a manual production approval gate.
Six layers of defence-in-depth: zero-trust default-deny NetworkPolicies, IRSA least-privilege pod IAM, hardened non-root read-only containers, mTLS via cert-manager, seven Kyverno admission policies, and IMDSv2.
Full observability — Prometheus metrics, a 35-panel Grafana dashboard, three SLOs backed by multi-window burn-rate alerting, and Kubecost for FinOps.
Nightly encrypted S3 backups with two tested recovery paths (app/config from Git via Argo CD, data from S3) documented in a runbook proven to restore in under two hours.
Published write-up. The build was written up as a ~6,000-word engineering article, “We Replaced a £100k/Year Manual Workflow With a £198/Month Kubernetes Platform — Here’s How” (19 June 2026), co-authored by the four of us and published on a teammate’s Medium account. It walks through the client scenario, the architecture decisions and the cost model.
Team project. Delivered as a four-engineer team (Samuel Onyejekwe, John Babalola, Seun Okegbola, Chinedu Izuelu) for the Cloudboosta Advanced DevOps cohort, June 2026.
Every lab and assignment from the Cloudboosta Cloud Computing and Advanced DevOps programmes — 34 write-ups totalling 1,207 pages, each with the objective, the steps taken, the commands run and screenshot evidence of the result. Filter by technology, then open any PDF to verify the work.
Showing 34 of 34 documented labs
Networking on Cloud · Class 2
Linux Command-Line Fundamentals
Create, inspect, concatenate and manage files and directories from the shell — the foundation every deployment script rests on.
LinuxUbuntuBash6 pages · 1 Mar 2026Open PDF Networking on Cloud · Class 2
Custom Dual-Stack VPC with EC2 Apache Web Server
Build a custom IPv4/IPv6 VPC (10.0.0.0/16) with public and private subnets, NACLs, route tables and an internet gateway, then provision an EC2 instance running Apache.
VPCSubnetsNACLSecurity GroupsRoute TablesIGWEC2IPv614 pages · 1 Mar 2026Open PDF Networking on Cloud · Class 2
Jenkins Server Provisioning on a Custom VPC
Provision a custom VPC and launch an EC2 instance to host a Jenkins automation server, opening only the ports the service actually needs.
JenkinsVPCEC2Security GroupsPort 808018 pages · 1 Mar 2026Open PDF Microsoft Azure Intro · Class 3
Set up a Python environment in VS Code and work through variables, arithmetic, type conversion and formatted output.
PythonVS CodeUbuntuf-stringsType conversion6 pages · 17 Mar 2026Open PDF Python Intro · Class 4
Python Lists, Slicing & Dictionaries
Build and slice lists, construct dictionaries and navigate the official Python documentation to solve problems independently.
PythonListsSlicingDictionariesPython docs6 pages · 17 Mar 2026Open PDF High Availability · Class 4
Application Load Balancer + Auto Scaling for High Availability
Deploy an internet-facing ALB and an Auto Scaling Group across two Availability Zones so the infrastructure recovers from instance failure with no manual intervention.
ALBAuto ScalingMulti-AZTarget GroupsHealth ChecksVPC53 pages · 17 Mar 2026Open PDF High Availability · Class 4
Design and deploy a segmented three-tier architecture — public web tier, private app tier and private RDS MySQL — with two NAT gateways for zone-local egress and strict tier-to-tier security groups.
3-TierVPCNAT GatewayALBAuto ScalingRDS MySQLSecurity Groups70 pages · 17 Mar 2026Open PDF Azure App Service · Class 5
Stand up an HR web portal isolated in a VNet, restrict access with NSG rules, and replace shared passwords with Entra ID identities and RBAC role assignments.
AzureVNetNSGEntra IDRBACLeast privilegeUbuntu VM46 pages · 22 Mar 2026Open PDF Azure App Service · Class 5
Azure App Service + Key Vault with Managed Identity
Remove secrets from code entirely — store the database connection string in Key Vault and let a system-assigned managed identity read it, so stolen source code grants no database access.
Azure App ServiceKey VaultManaged IdentityRBACSecrets38 pages · 22 Mar 2026Open PDF Azure App Service · Class 5
Model a four-table order schema in Azure SQL and process real orders with a serverless function that runs only when an order arrives.
Azure SQLAzure FunctionsHTTP triggerBusiness logic31 pages · 22 Mar 2026Open PDF Serverless Computing & Database · Class 6
AWS Lambda — Blueprint and From-Scratch Functions
Create Lambda functions both from a blueprint and from scratch, drive them with test events, and debug and fix runtime errors.
AWS LambdaTest eventsDebuggingPython15 pages · 1 Apr 2026Open PDF Serverless Computing & Database · Class 6
EC2 + Amazon RDS MySQL with Layered Security Groups
Provision a WordPress-ready architecture — an application security group for internet traffic and a separate database security group permitting only MySQL from the app tier.
EC2RDS MySQLSecurity GroupsEndpoints22 pages · 1 Apr 2026Open PDF Serverless Computing & Database · Class 6
WordPress Deployment on EC2 with an RDS Backend
Install and configure Apache and WordPress on EC2 and point it at a managed Amazon RDS database rather than a local one.
EC2ApacheWordPressRDSSSHSession Manager16 pages · 1 Apr 2026Open PDF Serverless Computing & Database · Class 6
Lambda-Driven EC2 Lifecycle Automation with boto3
Write Lambda functions that stop, start and terminate EC2 instances programmatically, backed by a purpose-built IAM role.
AWS Lambdaboto3IAM rolesEC2Python23 pages · 1 Apr 2026Open PDF Serverless Computing & Database · Class 6
Build an end-to-end event-driven pipeline: an upload to the source bucket fires a Lambda that resizes the image and writes the thumbnail to a destination bucket.
S3 eventsAWS LambdaIAMCloudWatch LogsImage processing23 pages · 1 Apr 2026Open PDF Git & GitHub · Class 7
Provision an S3 bucket with Terraform through a GitHub Actions pipeline, store AWS credentials as encrypted secrets, then ship a versioning change via a branch and pull request.
TerraformGitHub ActionsGitHub SecretsS3VersioningPull requests84 pages · 30 Apr 2026Open PDF
Install the AWS plugin set, store AWS credentials inside Jenkins, set the target region, and prepare a pipeline project for AWS deployments.
JenkinsAWS pluginsCredentialsRegionsPipeline project30 pages · 6 May 2026Open PDF Cloud Computing · Assignment 1
AWS CloudFormation — VPC, Subnets & RDS Subnet Groups
Author a CloudFormation template that provisions a production-style VPC with public, application and database subnets, deploy it from S3, and validate the stack events, resources and outputs.
CloudFormationYAMLVPCNAT GatewayRoute tablesS3Aurora MySQLStack outputs89 pages · 6 May 2026Open PDF Cloud Computing · Assignment 2
Deploy a Multi-AZ Oracle RDS instance with custom parameter and option groups, reach it from an EC2 command host over SSM Session Manager, and create tables with SQLPlus.
RDS OracleMulti-AZParameter groupsOption groupsSSM Session ManagerSQLPlus44 pages · 6 May 2026Open PDF Jenkins 2 · Assignment 1
Jenkins CI/CD Environment on a Custom VPC with NAT Gateway
Build the whole CI/CD environment from the network up — VPC with public and private subnets, IGW and NAT gateway, Jenkins on EC2, AWS credentials, Java/Maven toolchain and GitHub webhook integration.
JenkinsVPCNAT GatewayIGWJavaMavenGlobal Tool ConfigWebhooks49 pages · 14 May 2026Open PDF
Jenkins CI & CD Pipelines from SCM with Webhook Automation
Run continuous integration and continuous deployment as separate pipeline jobs driven by a Jenkinsfile in source control, triggered by webhook and gated by a deployment approval step.
Jenkins pipelineJenkinsfilePipeline from SCMWebhooksDeployment stagesApproval gate23 pages · 14 May 2026Open PDF
Jenkins Secrets Management & Role-Based Access Control
Store secrets in Jenkins' credential store, bind them into pipelines so they are masked in logs, and enforce least privilege with the Role-Based Authorization Strategy plugin.
Jenkins credentialsSecret textCredential bindingsMaskingRBACRole strategyUser accounts36 pages · 14 May 2026Open PDF Jenkins 2 · Assignment 5 of 5 · Week 3
Jenkins + Terraform Pipeline to Amazon EKS & ECR
Stand up Terraform remote state on S3 with DynamoDB locking, provision ECR and an EKS cluster, and drive container build and deployment from a Jenkins pipeline.
TerraformS3 backendDynamoDB lockingECREKSELBJenkinsDocker pipelineGitHub PAT84 pages · 19 May 2026Open PDF
Authenticate to Docker Hub from the CLI, tag and push images to a cloud registry, and demonstrate ENTRYPOINT behaviour and the running/exited container lifecycle.
Docker HubRegistryImage taggingApacheENTRYPOINTContainer statesdocker push19 pages · 23 May 2026Open PDF Docker 2 · Lab 1 · Week 5
Docker Swarm — Multi-Node Orchestration, Scaling & HA
Initialise a Swarm cluster across manager and worker EC2 nodes, deploy a multi-container stack, scale services, then drain a node and prove containers reschedule automatically.
Harden a Swarm environment end-to-end: scan images with Trivy, sign them with Content Trust, cap CPU and memory, drop unnecessary Linux capabilities, and manage secrets with mutual TLS and certificate rotation.
TrivyVulnerability scanningDocker Content TrustImage signingResource limitsLinux capabilitiesSwarm secretsmTLSCertificate rotation38 pages · 30 May 2026Open PDF
Verified
Credentials & awards
Academy certification, graded performance reports and academic degrees — all downloadable.
Most Consistent Student Award
Cloudboosta Academy · 2026 Cohort 1
20 June 2026
Awarded for sustained consistency and engagement across the full programme.
Final Performance Report — Cloud Computing & DevOps
Cloudboosta Academy · overall programme grade
17 weeks · issued 3 July 2026
A+ · 90.38%
The cumulative assessment across both the Cloud Computing and Advanced DevOps cohorts — 1,324 of 1,465 points spanning attendance, labs, assignments, quizzes, video posts and two project presentations (80.00% and 88.89%). Soft skills scored 22/25, with full marks for consistency, resilience and class engagement. Cloudboosta's pass mark is B- (60%); A+ requires 85%+.
The foundation-stage report covering AWS and Azure core services, networking, Linux, Python and serverless — superseded by the final overall report above.
Seven self-recorded videos covering the programme end to end — what I learned, what I built, and the reasoning behind each architectural decision. The clearest way to judge how I communicate technical work. Project-specific walkthroughs sit with their projects above.
Design and deliver technical training and onboarding programmes for engineers at major clients including Shell and Saipem, producing reusable course material and process documentation.
Coordinate cross-functional delivery and knowledge transfer on specialised engineering software — programme authenticated by IMarEST.
Subsea Structural Engineer
Aug 2019 – Mar 2020
International Energy Services Ltd (IESL) — Lagos, Nigeria
Delivered rigorous analysis and detailed technical documentation, improving reliability by 20% and cutting project review times by 25% through repeatable, well-documented processes.
Planned and ran inspection projects with Gantt scheduling, backlog management and risk assessment — delivering 15% ahead of schedule with zero safety incidents.